AppRiver (Zix) Email Authentication Guide: SPF, DKIM, and DMARC

by
Last Updated:
5 min read

by
Last Updated:
Key Takeaways
When your organization relies on AppRiver (now part of Zix) for cloud email security, hosted Exchange, or secure outbound relay, your messages are dispatched through AppRiver’s EdgePilot delivery infrastructure.
Without verified DNS authorization, receiving mail systems (like Google and Yahoo) cannot confirm that your domain authorized AppRiver to route messages on your behalf. Implementing an aligned SPF, DKIM, and DMARC policy cryptographically proves message authenticity, prevents domain spoofing, and secures reliable inbox placement.
If AppRiver handles outbound email relay or hosted Exchange for your domain, configuring these authentication protocols provides critical operational safeguards:
SPF defines which IP ranges and mail servers are permitted to send messages using your domain name. AppRiver uses the EdgePilot infrastructure for outbound routing.
If your domain does not have an active SPF entry in DNS, create a new TXT record in your DNS management console (e.g., Cloudflare, GoDaddy, Route 53):
v=spf1 include:edgepilot.com ~all
(Note: We recommend utilizing ~all (soft fail) during initial deployment rather than -all to ensure mail delivery is not disrupted while all sending sources are inventoried).
If your domain already sends mail through other platforms (such as Microsoft 365, Google Workspace, or Amazon SES), never publish a second SPF record. Publishing multiple SPF TXT records violates standard RFC specifications and results in an immediate PermError.
Instead, edit your existing TXT record and insert include:edgepilot.com right before the closing mechanism:
v=spf1 include:spf.protection.outlook.com ~all
v=spf1 include:spf.protection.outlook.com include:edgepilot.com ~all
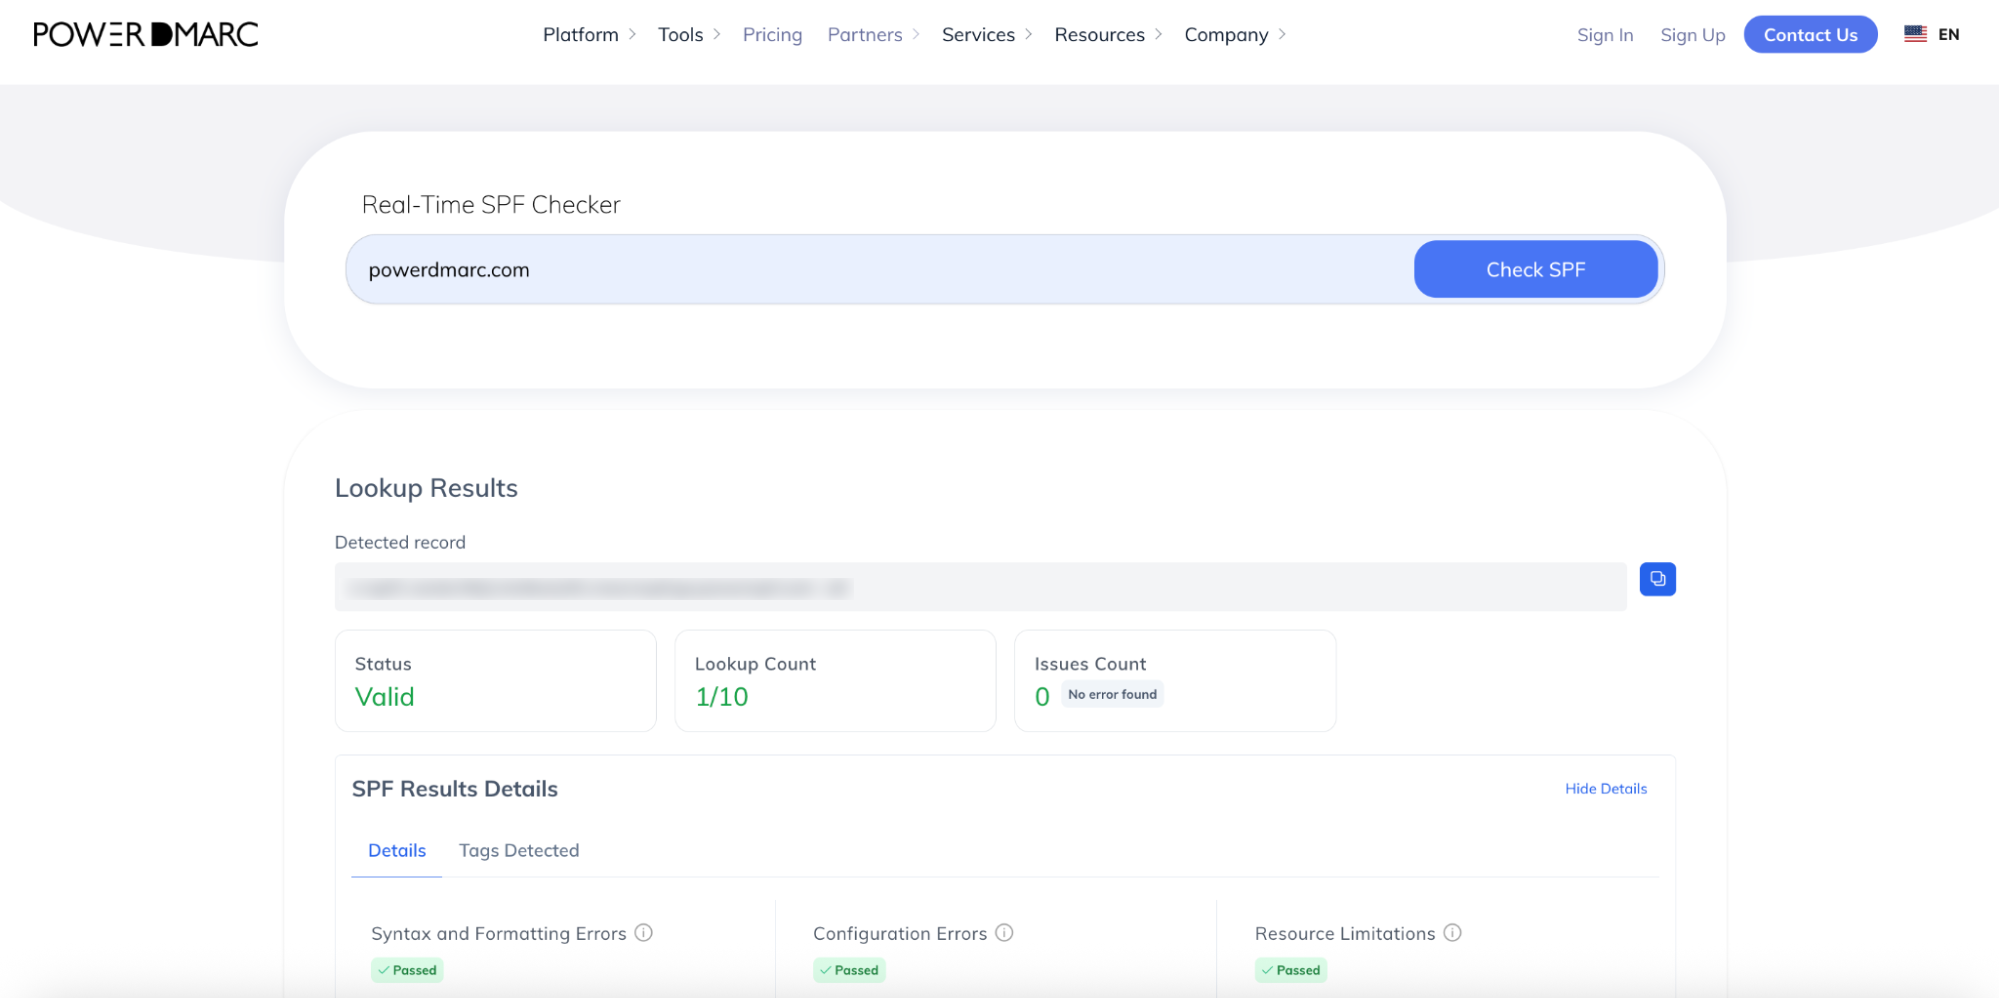
Pro Tip: Keep an eye on your DNS lookup count. SPF permits a maximum of 10 DNS lookups. If your organization utilizes multiple outbound marketing or transactional tools, consider utilizing PowerDMARC’s Hosted SPF / SPF Flattening to compress your lookups and prevent authentication failure. You can audit your current lookup count anytime using PowerDMARC’s SPF checker.
DKIM provides cryptographic assurance that an email message originated from your domain and remained untampered with during transit. While SPF authenticates the sending server, DKIM signs the actual message headers and body.
AppRiver coordinates unique cryptographic key pairs on an account basis.
1. Contact the AppRiver Support Team (via your admin portal or at [email protected]).
2. Request custom DKIM signing for your sending domain.
3. The support team will provide you with:
Once you receive the selector and key details, sign in to your DNS provider and add the required record:
v=DKIM1; k=rsa; p=[public-key-provided-by-appriver]
(Note for Cloudflare users: If AppRiver provides a CNAME record, ensure that the Proxy Status is set to DNS Only (Grey Cloud) to avoid authentication errors).
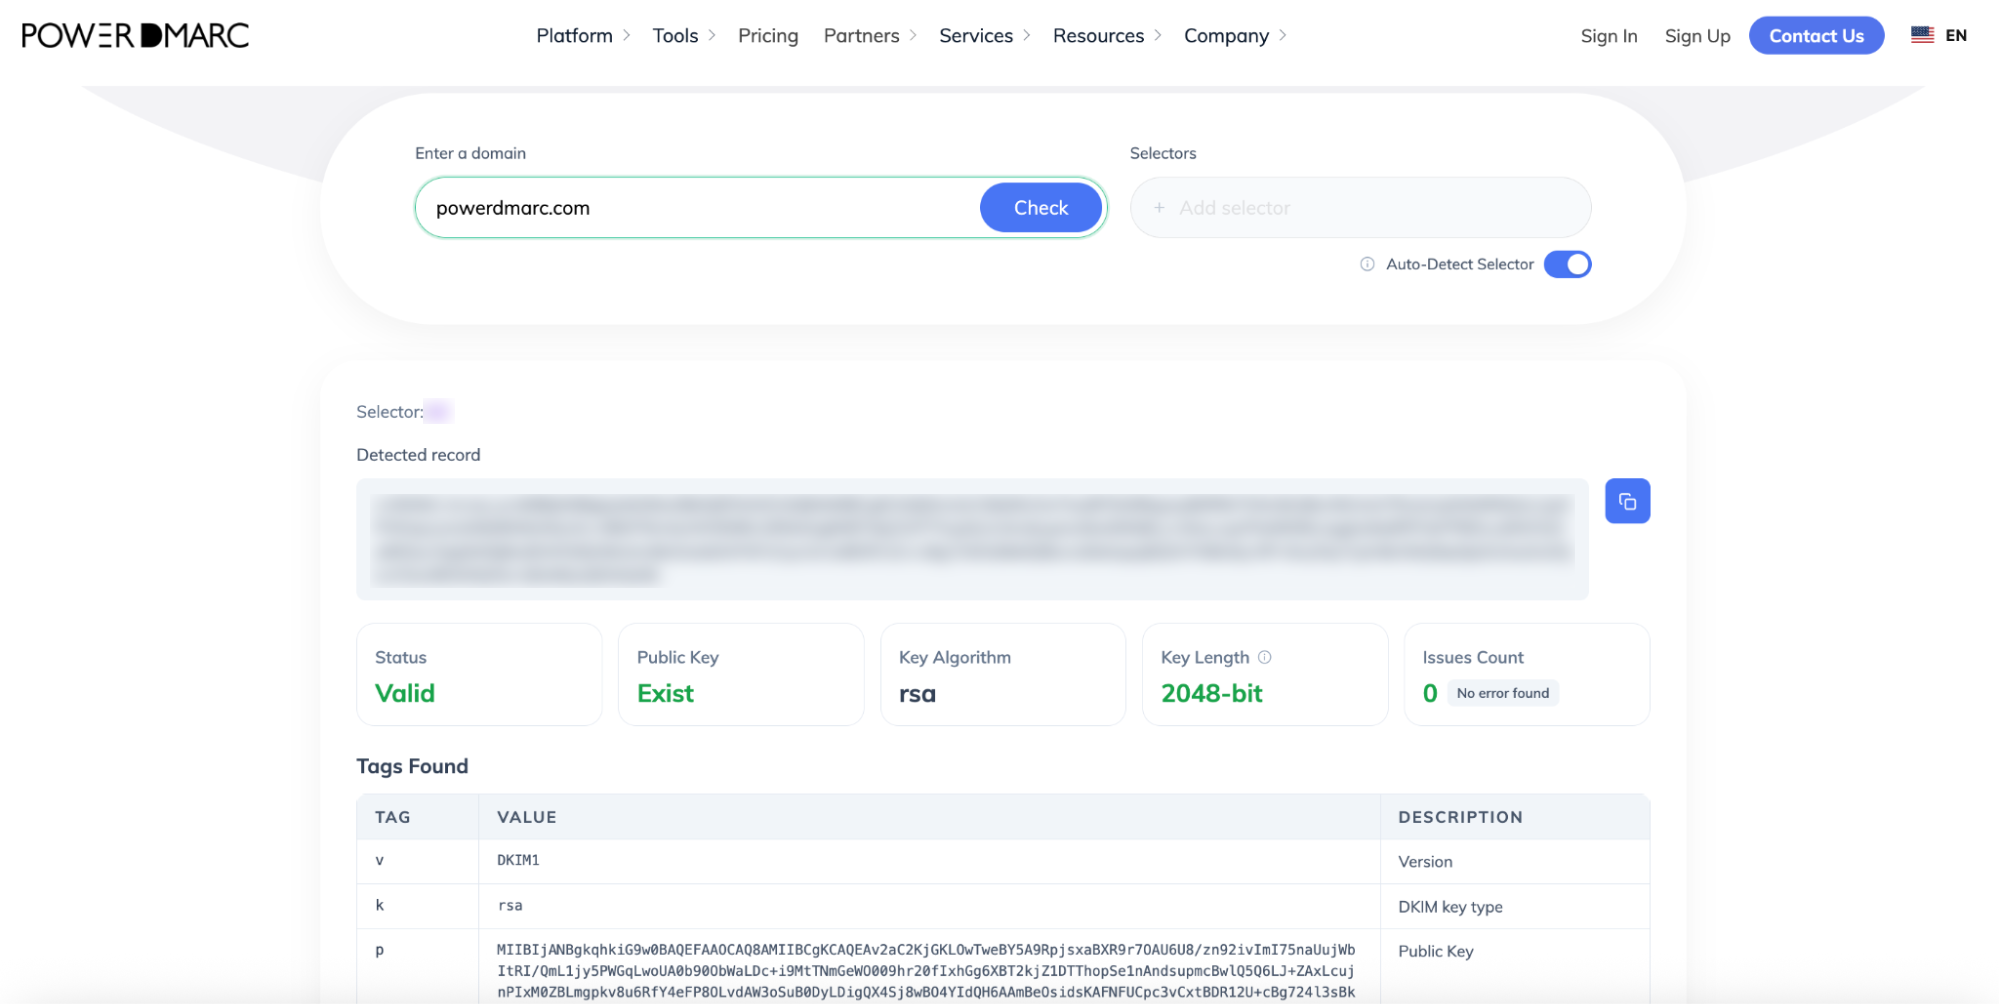
Notify AppRiver support that your DNS record has been published so they can toggle outbound signing for your account. Once confirmed, use PowerDMARC’s DKIM checker to verify that your selector resolves correctly.
With SPF and DKIM configured, you must implement DMARC. DMARC instructs receiving mail servers how to treat incoming messages that fail SPF or DKIM checks, providing full visibility into domain activity.
Use PowerDMARC’s free DMARC Record Generator to build your starting record.
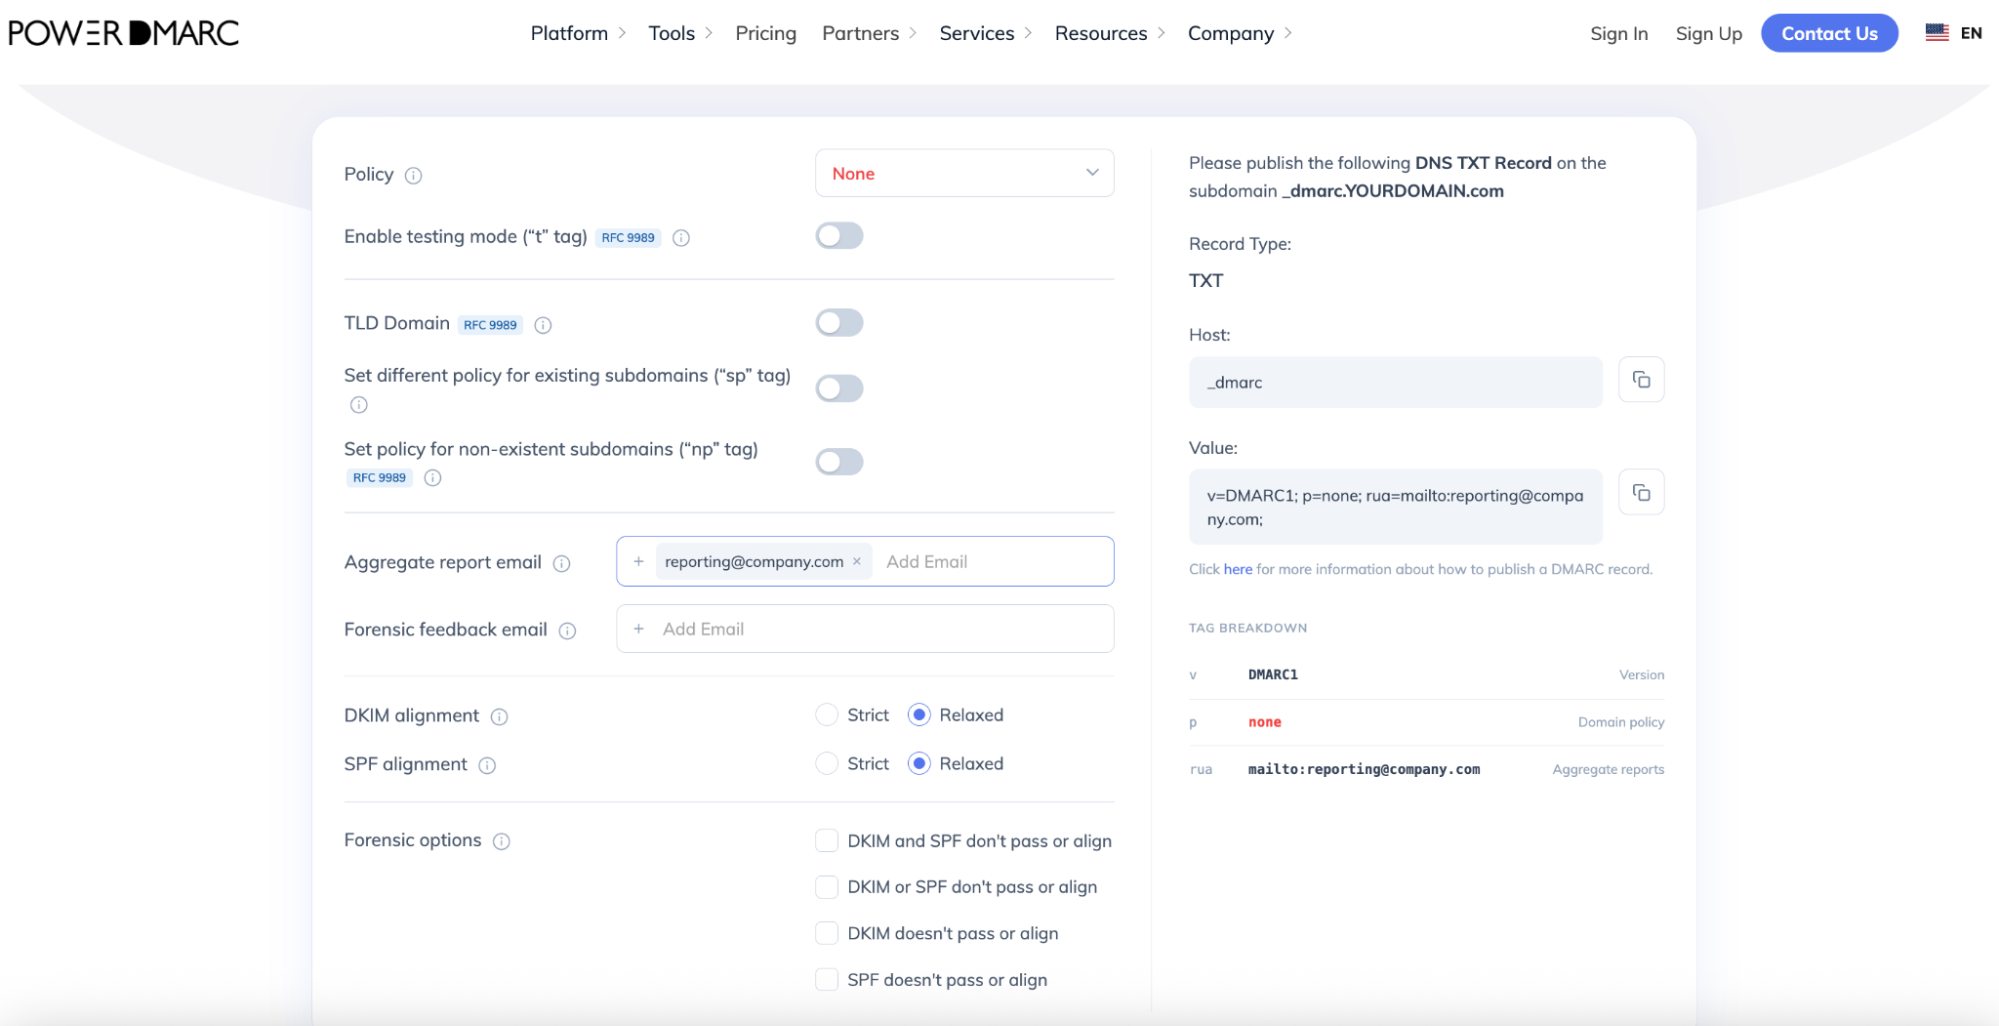
1. Access your DNS settings and create a new record:
2. Save your record.
Starting with p=none allows you to monitor all email sent on behalf of your domain without rejecting or quarantining legitimate business emails while your setup is finalized.
DNS changes can take between 15 minutes and 24–48 hours to propagate globally.
1. Run a Domain Health Check: Validate your published records using PowerDMARC’s free DMARC Record Checker.
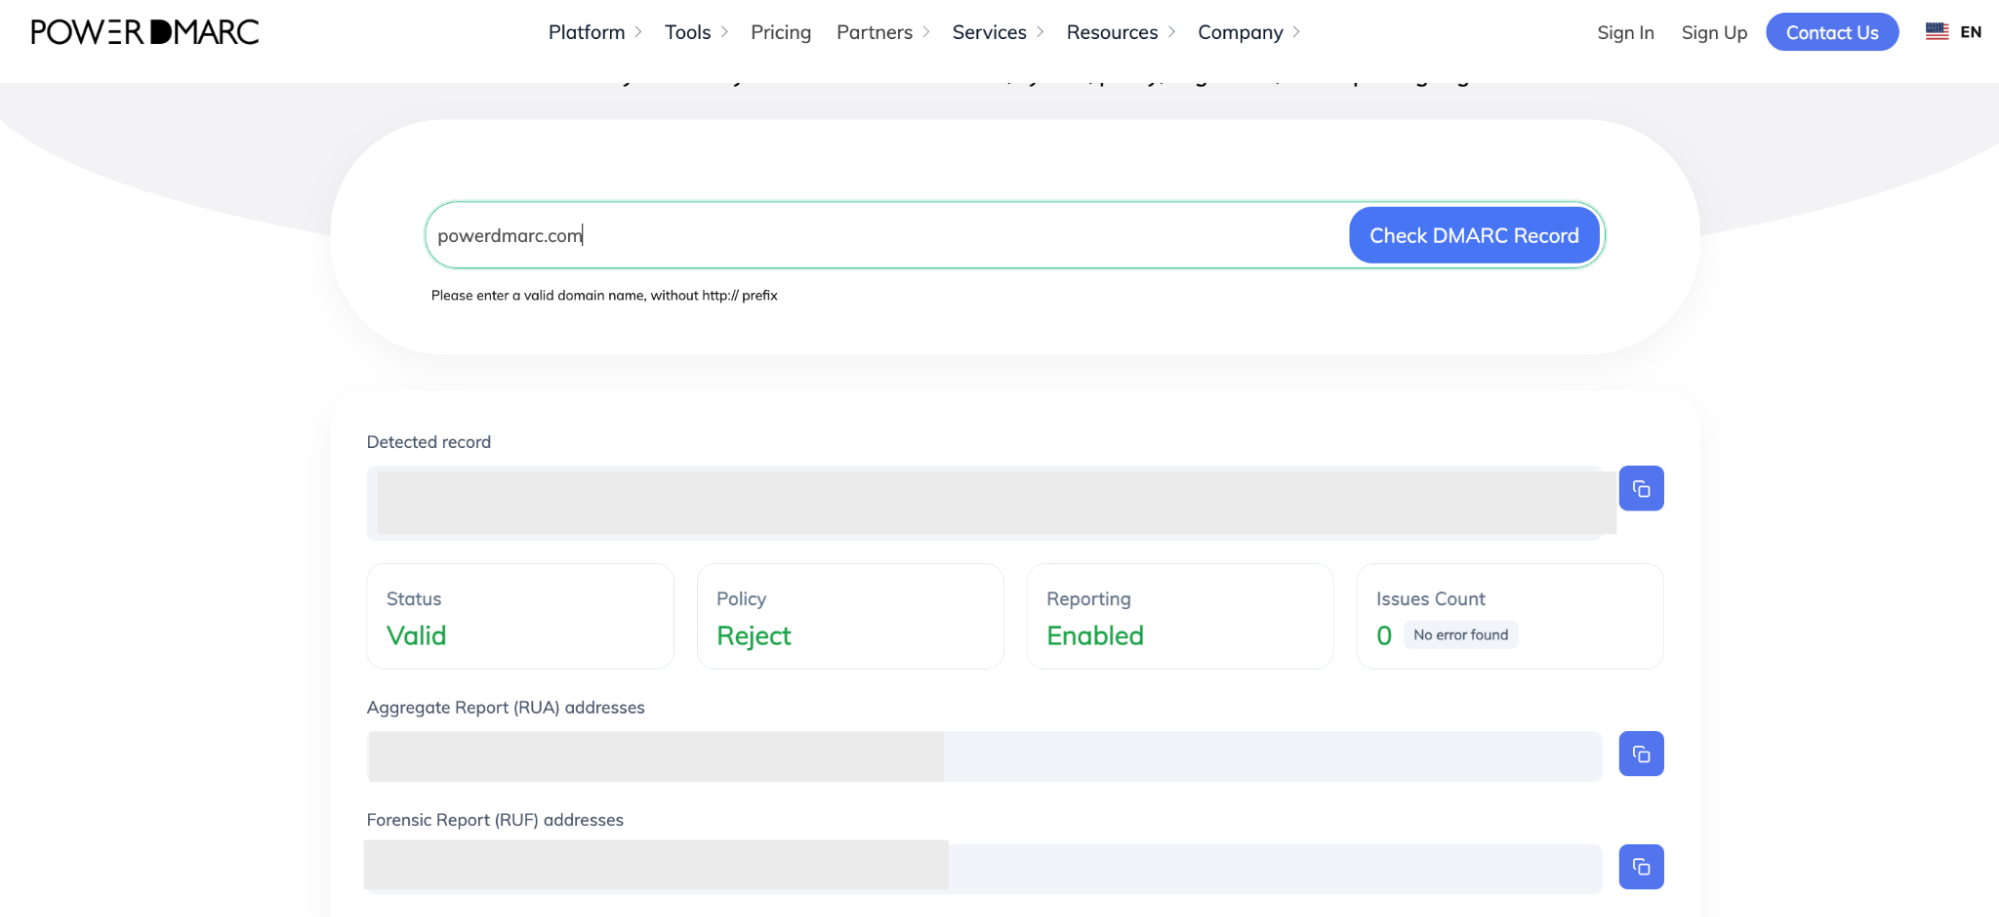
2. Send a Live Test Email: Dispatch a test email through your AppRiver outbound service to an external account (e.g., Gmail).
3. Inspect Message Headers: Open the raw headers (“Show original”) and inspect the Authentication-Results field:
Once your PowerDMARC aggregate reports confirm that 100% of your legitimate outbound traffic via AppRiver and other tools consistently passes aligned SPF and DKIM, you can transition to enforcement:
Ready to maximize your email security? PowerDMARC helps organizations seamlessly monitor AppRiver outbound streams, eliminate SPF lookup limits with automatic flattening, and safely transition to full DMARC enforcement.
Reach out to our team or book a PowerDMARC demo today to secure your business communications!